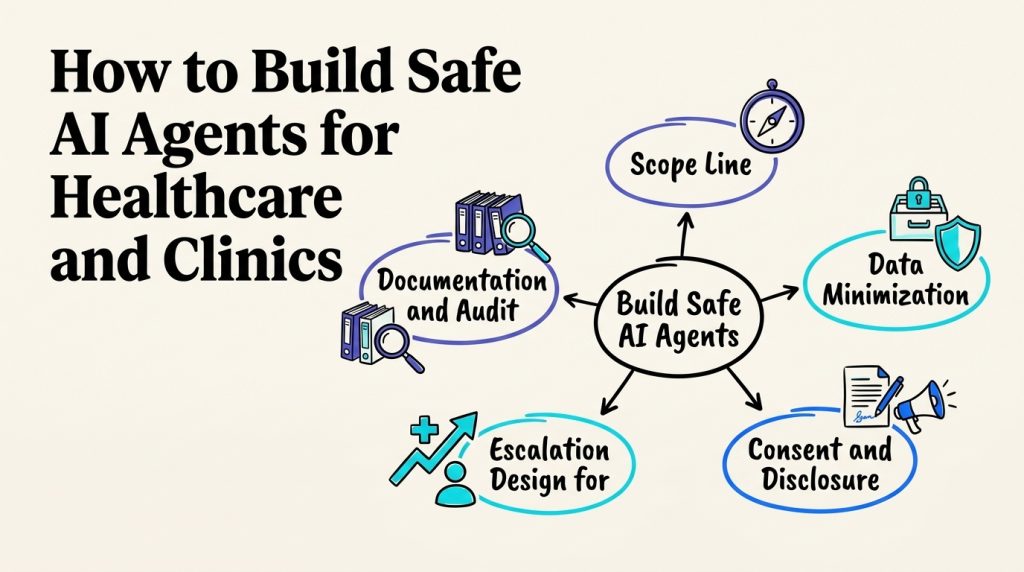
Safe AI agents for healthcare require a narrower operating boundary. Healthcare is the highest-stakes context for AI agents. A wrong answer isn’t an embarrassment, it’s a potential HIPAA violation, a misinformed patient, or a liability event. The design constraints are stricter, and the payoff is real: fewer missed calls, fewer no-shows, and front-desk staff actually doing front-desk work.
This playbook covers the healthcare-specific safety layer: data minimization, consent, escalation, and documentation.
Core idea: In healthcare, the agent’s job is narrow, answer non-clinical questions, book appointments, and get anything sensitive to a human fast. Everything else is out of scope by design.
Safe AI Agents for Healthcare: Set the Scope
Draw the line explicitly and put it in writing:
| Agent CAN | Agent CANNOT |
|---|---|
| Answer hours, location, parking | Any medical advice |
| Book, reschedule, cancel appointments | Diagnose or interpret symptoms |
| Explain insurance acceptance at a high level | Recommend treatment options |
| Confirm what to bring to an appointment | Answer “should I take my medication?” |
| Share preparation instructions from provider docs | Interpret test results |
Everything on the “cannot” list escalates to a human, with no clever phrasing exceptions. Keep the allowed scope as narrow as an AI appointment booking agent used for scheduling.
Explore Clinic AI Workflows with Botsify
See how Botsify can support booking and customer communication workflows.
Data Minimization
The core principle: the agent should know the minimum needed to do its job.
| Data type | Access |
|---|---|
| Appointment time and location | Yes, needed for booking |
| Name and contact | Yes, needed for scheduling |
| Insurance carrier (for verification) | Only if explicitly configured |
| Diagnosis or treatment details | Never |
| Payment details | Never through the agent |
This is both a design choice and often a legal one. If your practice is covered by HIPAA, document every data decision using HIPAA-compliant AI receptionist safeguards and an AI FAQ agent knowledge base built around approved information.
Consent and Disclosure
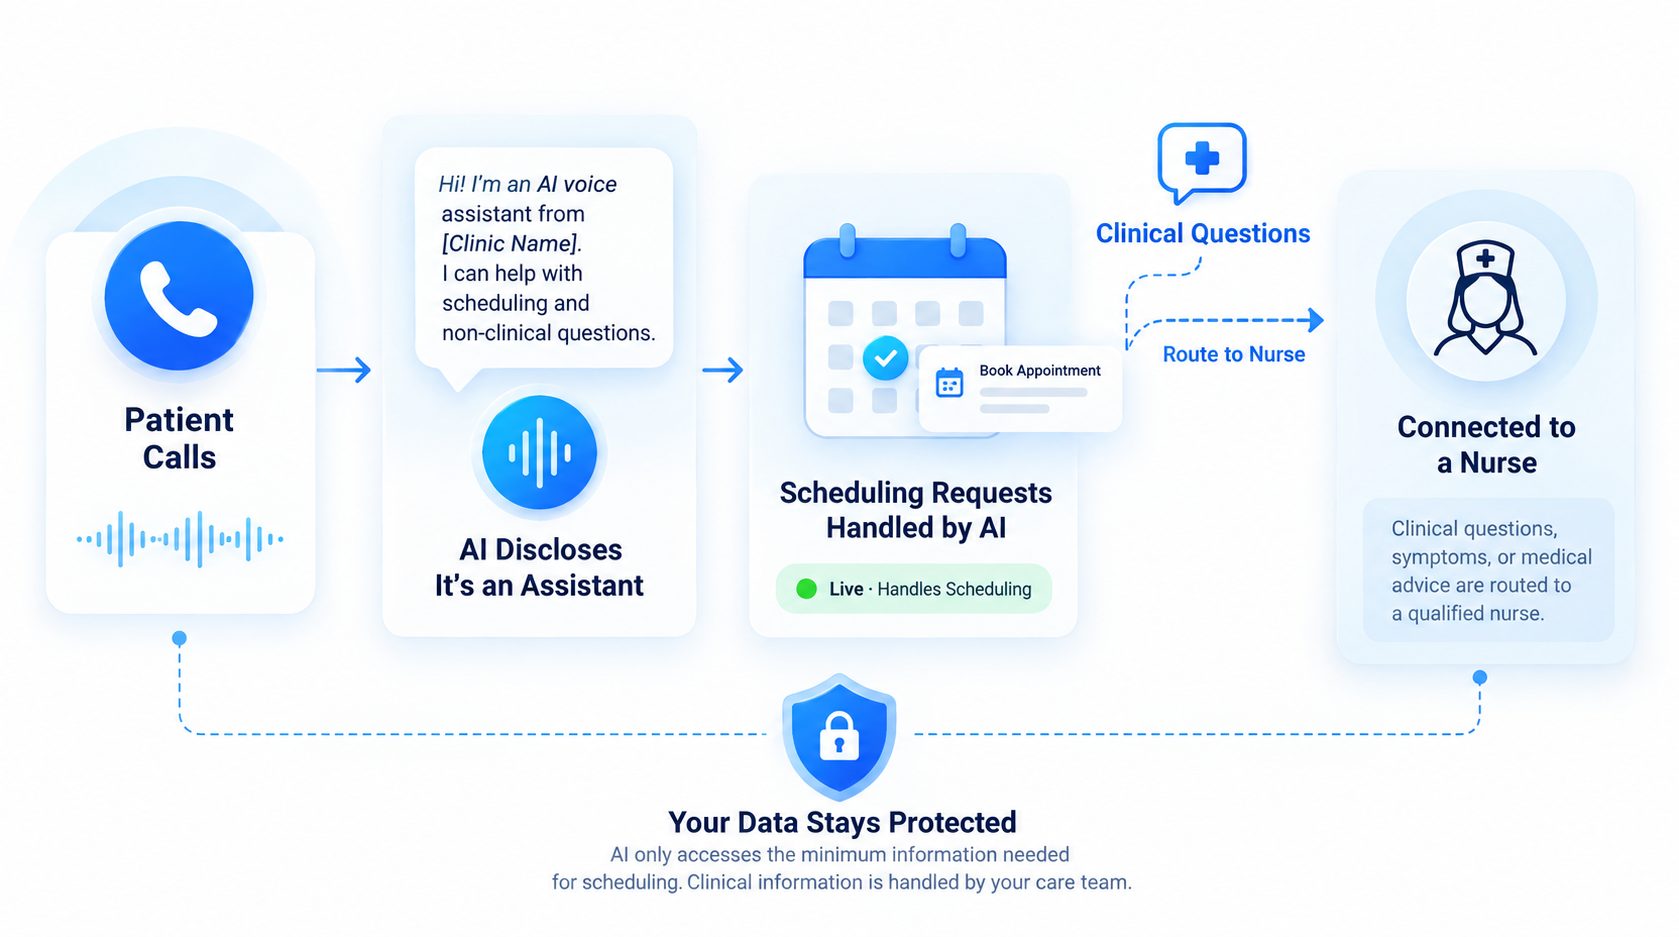
Patients should know they’re talking to AI:
- Disclose at the start of the conversation, “This is an AI assistant for scheduling, not medical advice”
- Offer a human alternative, visible, not buried
- Document consent for any data collection, the AI agent requirements
- Record retention policy, how long conversations are kept, and who can access them
This is both ethical and increasingly a legal requirement. Build it into the design, not as an afterthought.
Escalation Design for Clinics
| Signal | Route to |
|---|---|
| Any medical question | Nurse line or on-call provider |
| Urgent symptoms | Emergency instructions + immediate human |
| Billing dispute | Billing team |
| Prescription questions | Pharmacy or prescriber |
| Complaint about care | Practice manager |
The agent should never attempt to answer anything clinical, even “obviously simple” questions. Patients who self-diagnose with AI assistance are a liability you don’t want, regardless of whether the deployment includes multilingual AI agents.
Documentation and Audit
Healthcare context requires a stronger audit trail than typical support:
- Every conversation logged with timestamp and channel
- Every escalation recorded with reason and handler
- Access logs, who viewed patient-related conversations and when
- Retention policy, how long conversations are kept, and where
- Consent records, documented for any data use beyond the immediate conversation
Document the log structure through AI agent governance, then apply those policies throughout the AI agent lifecycle.
Staff Training
The front desk needs to know:
- What the AI handles (routine scheduling, FAQs)
- What triggers escalation (any clinical question)
- How to pick up an escalated conversation with context
- What to do when a patient is upset (the AI customer support agent)
Every front-desk person should read the AI agent implementation checklist before their first shift with the agent running.
The Patient Experience Standard
| Moment | Standard |
|---|---|
| First contact | AI answers routine questions in seconds |
| Clinical question | Routes to a human, no attempt at an answer |
| Booking | Confirmed immediately with details |
| Follow-up | Automated reminder, human for rescheduling |
| After hours | AI handles scheduling; emergency instructions and 911 guidance if needed |
The AI appointment booking agent pattern covers the scheduling flow; this adds the healthcare-specific boundaries.
Plan Your Healthcare AI Use Case
Talk with Botsify about a focused workflow for your clinic team.
FAQ
Can an AI agent give patients medical advice? No. That is a design boundary, so the agent routes every clinical question to a human under clear human handoff rules.
What about HIPAA compliance? Requirements vary by jurisdiction and configuration. Work with your legal advisor on what data the agent may access, and document those boundaries when planning AI agent integration.
What’s the biggest healthcare AI mistake? Trying to make the agent clinically helpful. It shouldn’t be, it should handle scheduling, hours, and logistics, and hand everything else to a human who has the training and the license.
Build a Safer AI Workflow
Explore Botsify for practical clinic automation with human support.
Final Thought
Safe AI agents for healthcare do one thing well: it makes sure routine questions are answered instantly and everything clinical reaches a human with context. Draw the line clearly, document the data rules, and build the escalation path first. That’s how you get the front-desk relief without the compliance headache.
